Security, Privacy & Deployment Architecture
How Identixia's on-premise architecture, data handling, and deployment options support your security and compliance requirements — stated at the claim strength the evidence actually supports.
Independently certified, audited and tested by third parties. See the full claim-by-claim breakdown below.
Security starts with where processing happens
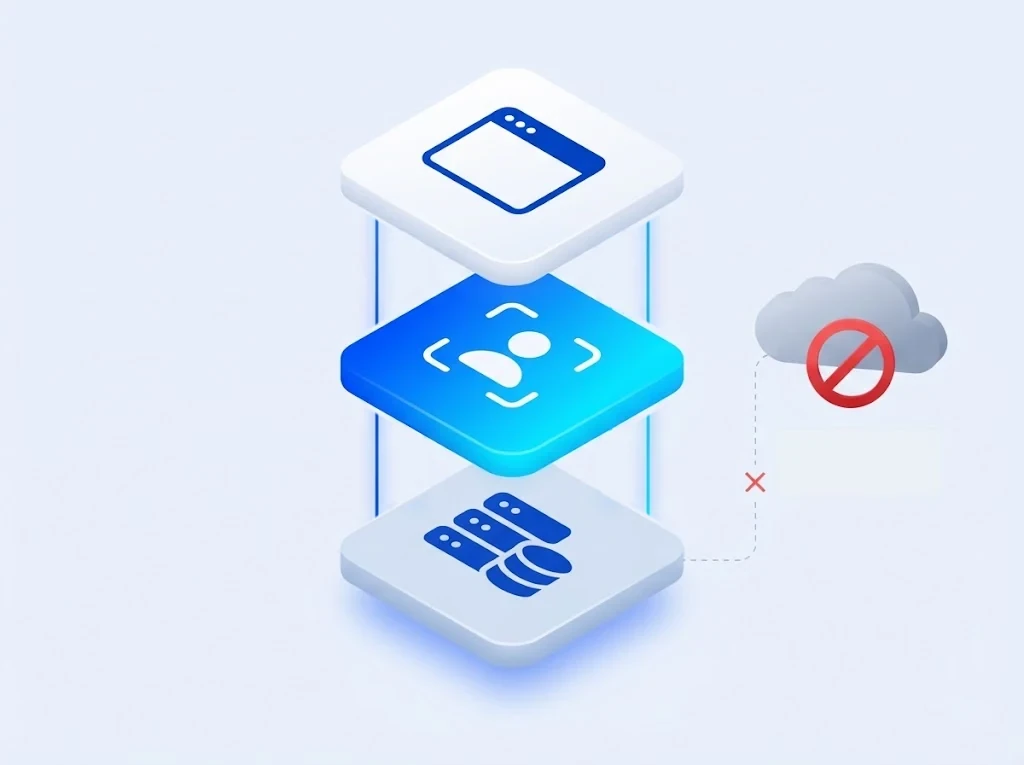
Identixia's SDKs are designed to run inside infrastructure you control — private cloud/VPC, on-device, offline where supported, or your own servers/containers. See the full breakdown on the On-Premise Identity Verification page.
What stays on your infrastructure
No mandatory transmission
On-premise deployment does not require sending document images, face images, or extracted biometric data to Identixia's servers.
You control retention
Because processing runs on your infrastructure, retention, deletion, and storage policies for verification data are set by your own systems, not by Identixia.
You control access
Access to verification data flows through your existing identity and access management, not a separate vendor-hosted system.
Four claim tiers, used precisely
Identity verification vendors often blur the difference between "certified," "tested," "supports a standard," and "designed for compliance." We don't. Here's what each tier means and where Identixia currently stands.
| Claim tier | What it means | Identixia's current status |
|---|---|---|
| Certified | An accredited third party has issued a certificate against a named standard (e.g. ISO 27001, SOC 2). | Certified — ISO/IEC 27001 certified; SOC 2 Type II audit completed against the Trust Services Criteria |
| Tested / evaluated | An accredited lab ran a specific test and issued a result. | Tested — presentation attack detection independently tested to the ISO/IEC 30107-3 methodology at iBeta Level 2 |
| Supports a standard | The product is technically built to work with a named specification, without a third-party audit. | ICAO 9303 machine-readable zone (MRZ) parsing and PDF417 barcode reading on ID documents — a technical accuracy claim, not a certification |
| Designed for compliance | Architecture choices that can help a customer meet their own obligations, without Identixia itself being audited against them. | Applies to on-premise deployment supporting data residency and access-control requirements your organization sets |
No new external dependency in your verification path
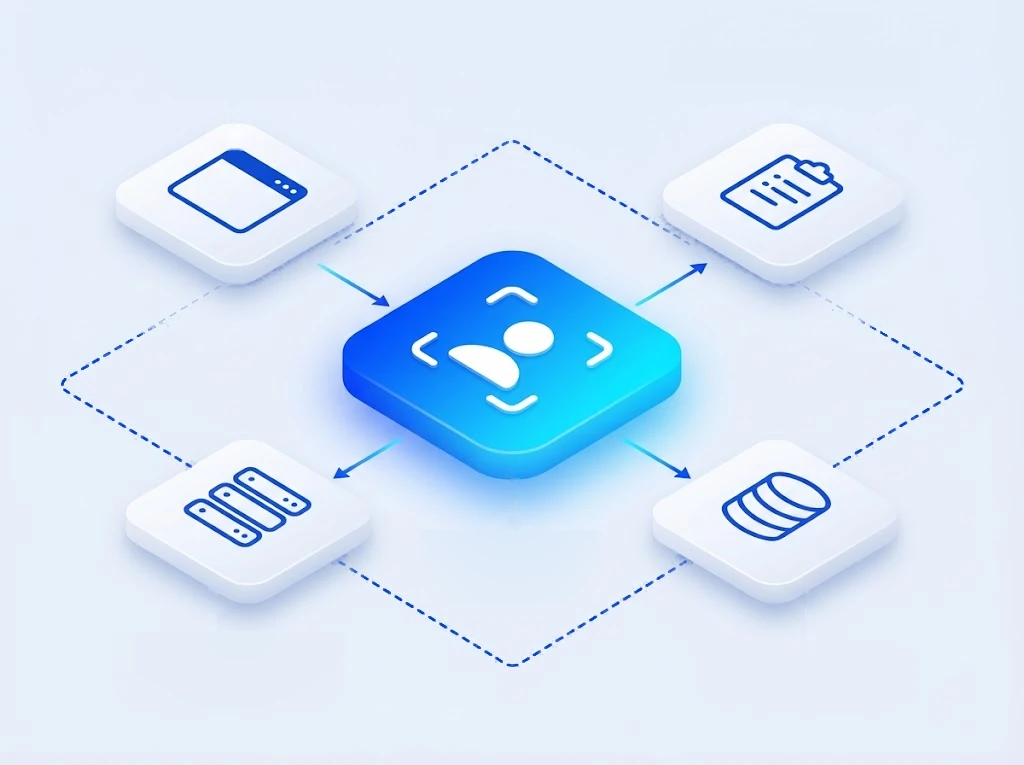
Because the SDKs run as software inside your environment, they operate within your existing network segmentation and security controls rather than requiring a new outbound trust relationship to a vendor-hosted endpoint.
Frequently asked questions
Request our security documentation
Get architecture diagrams and data-handling details for your review process.